Oak is an AI-native Identity Operating System that unifies identity discovery, governance, and access management across the enterprise. It connects human, machine, and AI-agent identities across cloud, SaaS, and on-premises environments to identify risks, enforce least privilege, and automate access remediation.
Key Capabilities:
- Unified Identity Discovery: Automatically discover and inventory human, non-human, and AI-agent identities across cloud, SaaS, on-premises, and custom applications.
- Identity Intelligence Layer: Build a unified identity graph connecting identities, permissions, resources, ownership, and access relationships across the enterprise.
- Non-Human Identity Security: Discover and govern service accounts, API keys, tokens, and machine identities, identifying unmanaged accounts, excessive permissions, and unowned credentials.
- AI-Agent Identity Governance: Discover AI agents and map their credentials, permissions, relationships, and human owners to improve oversight of autonomous workloads.
- Identity Governance & Administration (IGA): Support identity lifecycle management, access reviews, identity certification, and access governance across human and non-human identities.
- Access Intelligence & Entitlement Analysis: Analyze granted permissions and actual usage to identify excessive, unused, inherited, and indirect access privileges.
- Least-Privilege Enforcement: Reduce unnecessary access by identifying overprivileged identities and right-sizing permissions according to usage patterns and business requirements.
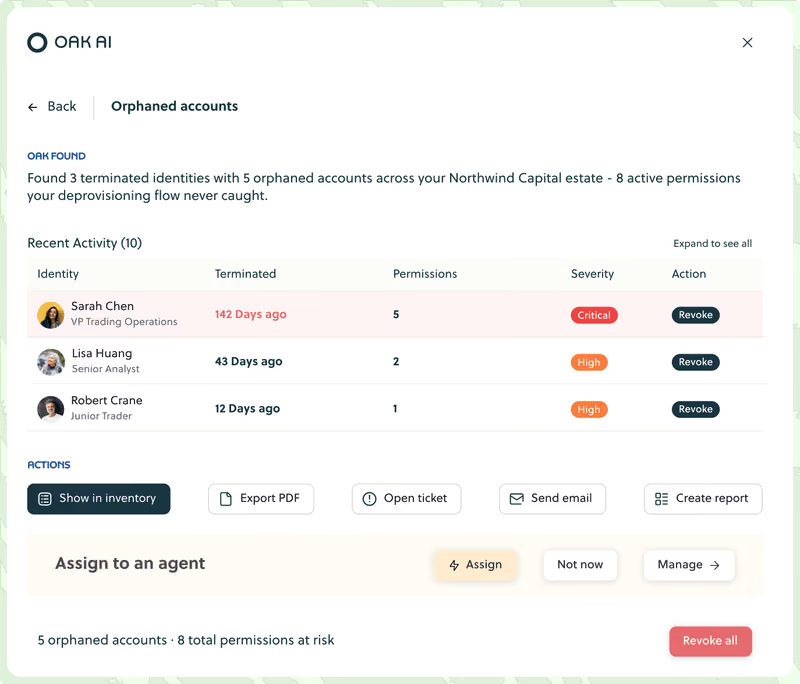
- Automated Access Remediation: Address identity risks by removing inappropriate permissions and revoking unnecessary access, reducing manual remediation efforts.
Featured Content
New
Machine Identity Governance Best Practices, From Creation to Retirement
Read article ↗ NewWho Owns an Orphaned Service Account, and How to Assign One
Read article ↗ NewIdentity Governance in Financial Services, for Every Identity Type
Read article ↗ NewService Account Sprawl, the Risks and How to Measure Them
Read article ↗Further articles from Oak
Showing 20 articles
- API Key Rotation, the Lifecycle Controls That Hold Up
- Five Hops From a Fake Job Interview to $6.34 Billion Stolen From Crypto Giant Binance
- How to Inventory the AI Agents Running in Your Enterprise
- How to Govern MCP Servers in an Enterprise
- What SOC 2 Asks for on Service Accounts and Other Non-Human Identities
- What SOC 2 Type 2 Report to Ask an Identity Vendor For
- What Identity Governance Implementations Cost and How Long They Run
- Four Ways In: How ConnectAny Reaches Every Identity in Your Estate
- Build or Buy Identity Governance for AI Agents
- What to Require in an Identity Security Proof of Concept
- Replace Your IGA or Build on It? How to Decide
- How to Choose an Identity Governance Platform: A Buyer's Checklist
- You Can't Govern What You Can't Connect
- The Scariest Part of the First AI-Run Cyberattack Is That Nothing in It Was New
- One Phone Call. 148 Systems. £29 Million.
- 700 Companies Were Breached by a Chatbot Nobody Owned
- “Not a Security Incident.”
- Nothing Was Hacked. Everything Was Authorized.
- Oak comes out of stealth with $60M in Seed Funding to Build the AI-Native Identity Operating System
- Identity has plenty of tools. It never had an operating system.
No articles match these filters.
Deepen Your Knowledge
Free weekly newsletter
Subscribe to the NHI & AI Identity Journal
The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week.
Bonus 33% off our NHI Course when you subscribe.