Access Governance for Every Identity — Human, Non-Human, and Agentic
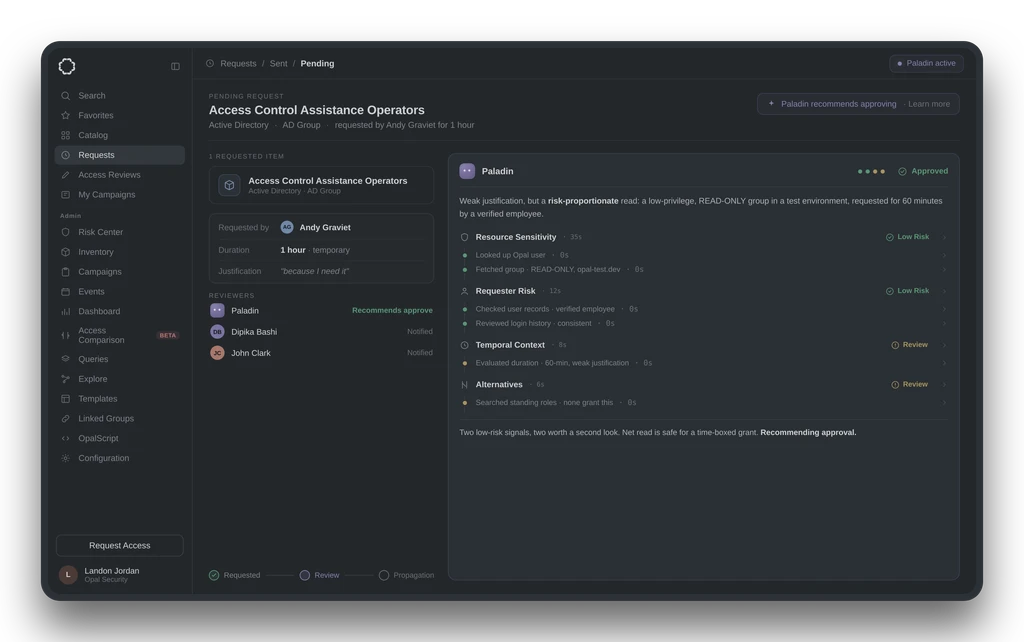
Opal is the access control plane for every identity. It builds a complete access graph across cloud, SaaS, databases, and AI platforms, then continuously enforces least privilege so standing access shrinks on its own. Service accounts, CI/CD pipelines, and API tokens are governed side by side with humans and AI agents, with an AI agent that approves safe requests, escalates only what needs a human, and revokes access the moment it’s no longer needed.
Key Capabilities:
- See every identity and path: Query your entire environment in plain English to surface over-provisioned access, SoD conflicts, and hidden privilege-escalation paths.
- Non-human coverage: Govern service accounts, CI/CD pipelines, and API tokens alongside human and agent identities.
- Security for AI agents: Define what agents can see, access, and execute before they touch your systems.
- Just-in-time access: Grant privileged access only when needed and revoke it automatically when the work is done.
- Programmable governance: Encode approval rules as version-controlled, testable policy that scales across every team.
Featured Content
New
Introducing Access Path Queries: Trace every person's and agent's access to its source
Read article ↗ NewOpal + Okta Cross App Access: Secure Agent Access to Opal MCP
Read article ↗ NewIntroducing Opal Zero: Q&A with CPO Sameer Mehta
Read article ↗ NewPaladin, Opalâs access agent, is now available in on-prem, self-hosted deployments
Read article ↗Further articles from Opal Security
Showing 45 articles
- New in Opal: Paladin, Access Campaigns, and OpalScript hit GA
- OAuth for Opal MCP: give agents access, not a standing key
- Paladin: AI that applies your policy to every request
- New in Opal: Access Comparison, Find and Fix Outlier Access Fast
- What's new in Opal's MCP servers: self-hosted, scoped, and approval-ready
- From Slack Request to Governed Grant: How Opal and Risotto Make Access Self-Serve
- AI-Guided Access Reviews, Now in Opal
- Access Has Outgrown Human Scale. We're Building the Governance to Match.
- Building What's Next: A Conversation with CPO Sameer Mehta
- Governing Access to Real-Time Analytics: How Opal and ClickHouse Secure Your Data at Scale
- Supercharging Identity with Opal and Databricks
- 10 Recent Breaches that Could Have been Prevented with Modern IGA
- From Detection to Resolution: How Opal and Rootly Secure On-Call Access
- Opal's Next Chapter: A Conversation with CEO Howard Ting
- Flexibility First: Four Classes of Custom Connectors for Engineering-Led Companies
- Identity Security and the AI Adoption Maturity Curve
- Customer Voices: How Mercariâs Security Team is Building Guardrails for the AI Era
- How Opal Streamlines Identity Lifecycle Management
- Skip the IdP Migration: Scale Identity Security Without the Overhead
- How Leading Teams Are Modernizing Authorization with Opal to Reduce Risk and Regain Control
- The Rise of Non-Human Identities: Why AI Agents Break Traditional Access Models
- How Legacy Access Models Create Systemic Risk: The Cost of Doing Nothing
- The Quiet Breach Vector: How Traditional Access Models Are Failing Security
- When Identity Gets Acquired, Authorization Gets Real
- Securing the Agentic Enterprise: Identity in the Age of Autonomy
- Unifying Identity Security in Your SIEM: How Opal and RunReveal Create Complete Security Visibility
- Scaling Security through M&A: How Opal Simplifies Access Management for Growing Organizations
- Better Security Inside the Front Gate: Fine-Grained, Time-Bound Access for AWS
- Authorization has always been the real perimeter
- Securing the Autonomous Future: Why We Built Opalâs Risk Layer
- Inside Opalâs Access Rules: Dynamic Attribute-based Access Management
- Identity Governance is a Security Problem, Not an IT Process
- 4 Actions to Reduce Group-Based Access Control Risk
- The Compliance Crossover: Identity Security Requirements Within Compliance Frameworks and Privacy Regulations
- Six Degrees of Identity Security Issues
- 3 Practical Changes to Refine Access Controls Without Being Overly Restrictive
- If Itâs Not Continuous, Itâs Not Secure: Reimagining Identity Management
- Least privilege security is important. But how do you actually implement it?
- Privileged Access Management: Gatekeeping for the Greater Good
- Authn and Authz: Two Sides of the IAM Coin
- When authorizing user access, what can and can't be automated?
- Collecting the right signals for intelligent authorization
- Why does user authorization matter more than identity?
- Custom App Integration
- How to Automate On-Call Access Management with Opal and PagerDuty
No articles match these filters.
Deepen Your Knowledge
Free weekly newsletter
Subscribe to the NHI & AI Identity Journal
The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week.
Bonus 33% off our NHI Course when you subscribe.