Core Capabilities
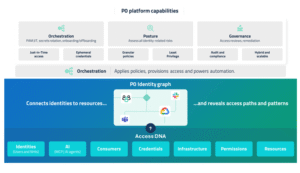
- Orchestration: Provisions ephemeral access via IAM APIs. Supports Just-in-Time (JIT) for users, scoped permissions for NHIs, and just-in-time credentials. Access requests flow through Slack, CLI, Microsoft Teams, or web UI with multi-step approvals and time-limited sessions.
- Posture analysis: Continuously evaluates blast radius, usage patterns, stale credentials, and excessive privileges. Surfaces the most exploitable risks across clouds.
- Governance: Enforces policy-as-code using the identity graph, automates access reviews, and integrates with frameworks like SOC 2 and ISO 27001 for full audit readiness.
Value by Role
- Security teams: Gain visibility into who has access, when, and why—plus automated least-privilege enforcement.
- Developers: Get scoped, time-bound access from inside familiar tools—no extra friction.
- Platform engineers: Replace brittle scripts with scalable access-as-code policies.
- CISOs: Eliminate standing access and measure risk reduction across identity types.
- Compliance teams: Automate evidence collection, approval trails, and entitlement reviews.
Featured Content
New
Nobody built MCP servers to hold identity. They do anyway.
Read article ↗ NewEvaluating agentic access control approaches
Read article ↗ NewControlling agent access beyond MCP gateways
Read article ↗ NewP0 Security corporate overview
Read article ↗OAuth scopes don’t equal secure MCP authorization
Read article ↗Non-Human Identities (NHIs) vs. Machine Identities: Key Differences & Security Best Practices
Read article ↗The OpenAI agent did not go rogue. It ran out of authorization boundaries.
Read article ↗Machine, workload, service—it doesn’t matter if it’s unsecured
Read article ↗Trends in cloud security from cloud to workloads
Read article ↗How a Leading Insurance Provider Secured 40,000+ Service Accounts in GCP
Read article ↗Redefining Security with Unified Identity Governance and Access Management
Read article ↗Strengthening Access Governance for Human and Machine Identities
Read article ↗Further articles from P0 Security
Showing 57 articles
- P0 Runtime Access platform for Agents
- Anatomy of an agentic outage
- Agent provenance is ambitious, so let’s get the hard parts right
- When your coding agent can commit everything you can commit
- Privileged access readiness pack
- Just-in-time RDP access
- Runtime agent controller
- Agents are redefining sensitive access and P0 is leveraging AI to extend coverage just as fast
- Why Authentication Is Not Enough For Agents
- From MCP Tool Filtering to Runtime Access Control
- The three types of JIT (And why only one actually kills standing access)
- Agentforce and Cortex aren’t SaaS features, they’re agent runtimes
- The Composio breach: Let’s stop blaming the agents
- Securing AI agents starts with governing human authority
- The identity risks of vibe coding
- Claude didn’t go rogue. Permissions did.
- When your Snowflake AI agent can query everything you can query
- 2026 SACR report
- 2026 SANS State of identity threats and defenses survey insights
- Right-size agent and service account access
- Anthropic’s Claude Enterprise
- The day “access” stopped meaning “login” and started meaning “authorization”
- Every era has its “worked great” tech. Then the environment changes.
- How to Sync AWS Access with ServiceNow
- Azure AI Studio and Azure OpenAI
- The ServiceNow AI breach: Why agentic access requires layered defense
- Technical Deep Dive: AuthZ Control Plane for Agents
- Google Vertex AI
- When Neha and Kelsey said the quiet part out loud about privileged access
- From Legacy to Cloud: Securing the Production Stack with API-led Access Management
- Defining and securing privileged access in modern environments
- Why broken access control still tops the OWASP Top 10 and what it means for identity security in the era of hybrid cloud
- Access in control: AWS Bedrock
- Governing Access in Amazon Bedrock
- Five minutes to secure OCI access with least privilege just-in-time provisioning
- Self Assessment: Modern Access Management Maturity
- Close the NHI Governance Gap
- Why PAM Needs to Evolve
- Start Governing NHIs by Managing Access, Not Credentials
- The rise of non-human identities and the future of PAM
- Why cloud-native demands an API-led approach to PAM
- Beyond Humans: Governing Machine Identity Access at Scale
- Secure by design: When agents enter production
- Outnumbered and Underprotected: The Hidden Risk of Non-Human Identities
- What’s driving the need for Zero Standing Privilege
- Ten things to understand when using agentic AI applications
- How to get just-in-time access to RDS Postgres
- How to fix standing access in AWS
- How to elevate machine identity permissions in GitLab Pipelines
- How to automate credential rotation with GCP and Jira
- How to enable JIT admin access for homegrown apps
- How to enable JIT access with Okta (Grafana example)
- IDAC podcast: How to flip from traditional PAM to JIT access
- Machine, workload, service—it doesn’t matter if it’s unsecured
- Production access is a mess. Here’s how to improve your journey.
- Rolling out/enforcing least privilege in practice in AWS/GCP/Azure
- Trends in cloud security from cloud to workloads
No articles match these filters.
Deepen Your Knowledge
Free weekly newsletter
Subscribe to the NHI & AI Identity Journal
The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week.
Bonus 33% off our NHI Course when you subscribe.