PlainID Runtime Authorization Platform
Centralize Authorization. Enforce It Everywhere.
One platform to discover, manage, and enforce authorization for every identity – human, non-human, and AI agent – across applications, APIs, microservices, data, and agentic AI.
Centralized policy management gives organizations consistency, visibility, and governance. Distributed decisioning and pre-built Authorizers enforce fine-grained access close to the resource, with the performance, resilience, and flexibility required for enterprise environments.
Discover
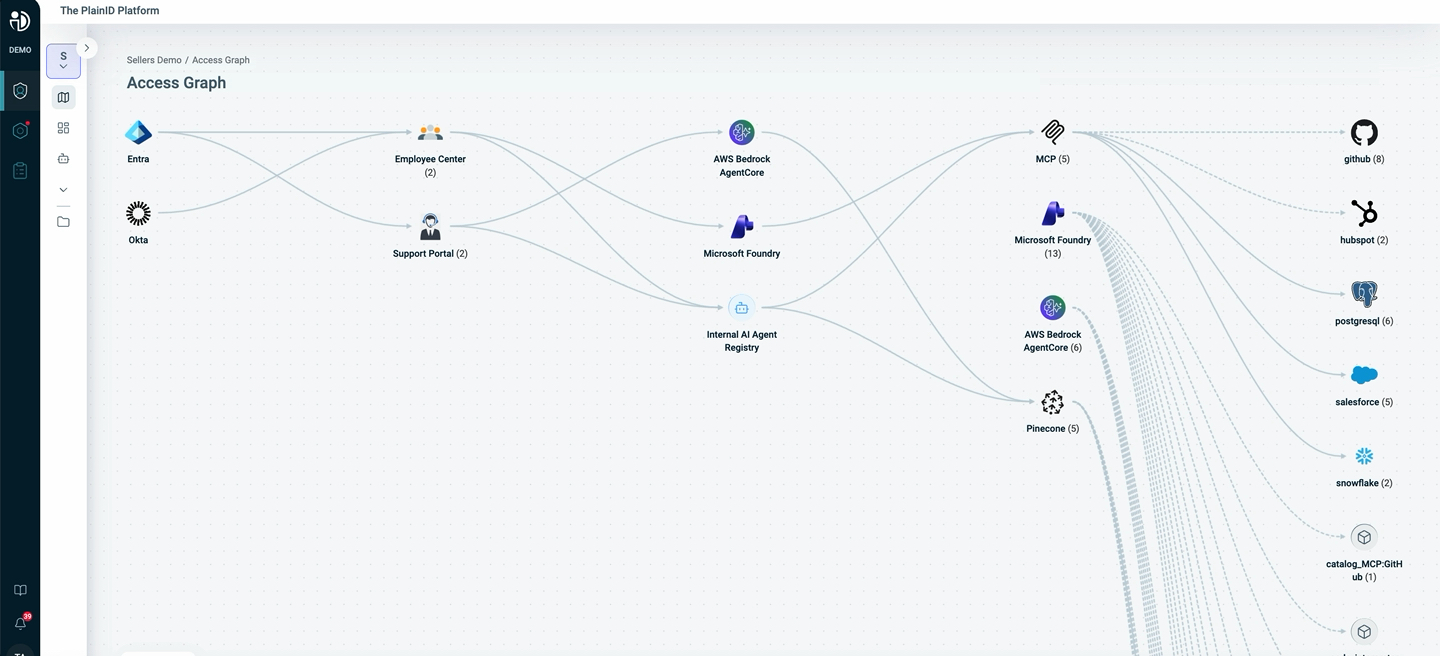
The Discover stage builds the context needed to write policy. It identifies and enriches identities, AI agents, resources, MCP servers, tools, APIs and data sources, and maps the access relationships between them. It can also discover authorization policies that already exist inside connected platforms, and adds ownership, purpose, sensitivity and risk context to what it finds. The platform surfaces both direct and indirect access paths.
Manage
The Manage stage is where policy is written and governed. Business and security teams can author policies in a visual interface, while developers can work with policy as code. Governance features include:
- Versioning, approvals and controlled promotion between environments such as staging and production
- A policy simulator for testing and impact analysis before changes go live
- Certification campaigns, audit reporting and business-readable explanations of decisions
- Delegated administration with separation of duties
- Policy360, a connected view of every policy, its dependencies and its change history
Enforce
The Enforce stage evaluates each request against policy using identity, resource, action, business, environmental and risk context. Decisions go beyond a simple permit or deny. Depending on the integration, PlainID can return allowed operations or entitlements, row and document filters, column and response masking, token claims and scopes, permitted tools for an AI agent, constraints on tool parameters, and obligations such as approval or step-up authentication.
Featured Content
Secure Every Identity Across Your Tech Stack
View event ↗ NewXACML, OPA, and PBAC: How to Modernize Legacy Authorization Without Rebuilding Everything
Read article ↗ NewAI Agent Identity Governance: How to Control Agents Before They Touch Sensitive Data
Read article ↗ NewNon-Human Identities Are Multiplying. How Do You Keep Machine Access Under Control?
Read article ↗Further articles from PlainID
- Agentic IAM Day 2026
- How to Build an AI Agent Permission Control Framework Security Teams Can Actually Audit
- Operationalizing Zero Trust: How Runtime Authorization Fulfills NIST SP 800-207 & SP 800-207A
- PlainID and the OWASP Top 10 for Agentic Applications (2026)
- How PlainID Tackles the OWASP Top 10 Vulnerabilities for LLM Applications
- Why Centralized Policy Management Breaks at Data-Layer Scale
- Access Control for AI: How to Stop Agents From Over-Permissioning Themselves
- Go Beyond Who Gets In: PlainID Launches a New Brand for the AI Era
- Go Beyond Who Gets In.
- PlainID Mentioned in the 2026 Gartner® Innovation Insight Report on IVIP and IAM Augmentation Vendors Disrupting Light IGA
- How runtime authorization helps turn EU AI Act requirements into enforceable controls
- What Is Dynamic Authorization?
- How to Get Started with Authorization Strategy
- From Security Control to Strategic Enabler: The Business Drivers Behind Modern Authorization
- Agentic IAM: A 5-Layer Architecture for Governing AI Agents
- AI Agent Authorization: Why Static Roles Break
- How Microsoft and PlainID Extend Trust Through Agentic Workflows
- SaaS Authorization: When Access Reviews Fall Behind
- What Is Relationship-Based Access Control (ReBAC)?
- What 20 Fortune 500 IAM Leadership Titles Reveal About the Agent Authorization Gap
- Runtime Authorization for Agentic AI: Fixing the Three Breakpoints in Legacy IAM
- Driving Interoperability: PlainID’s Native Integration with AuthZEN
- PlainID and Cisco Duo: Real-Time Authorization at SSO Sign-In
- How to Evaluate Enterprise Authorization Management Platforms for Complex Environments
- PlainID Brings Google BigQuery’s Native Data Controls Into One Control Plane
- Intent-Based Access Control for AI Agents
- Portable Trust: How Thales and PlainID Extend CIAM for Advanced Digital Business
- Feature Focus Series: Agentic AI Observability
- Feature Focus Series: Agentic AI Observability
- PlainID Named as a Sample Vendor in the Gartner® Hype Cycle™ for APIs, 2026
- Transforming Authorization into a Strategic Control Plane for the Agentic AI Era
- PlainID Expands Support for AWS AgentCore and Microsoft Foundry Across Its Agentic Security and Authorization Platform
- Enforce with PlainID Series: Securing OpenClaw With Runtime Authorization
- PlainID Named in the 2026 Gartner® Reference Architecture Brief: IAM for AI Agents and Other Workloads Report
- Protect Your Data from AI Agents Running in the Wild
- Enhance Zscaler ZPA with PBAC
- 10 Core Design Principles for Securing Agentic AI
- The Four AI Guardrails Every Agentic System Needs
- Zero Standing Privileges for Agentic AI
- Secure Agentic AI with Runtime Authorization
- Static Authorization Is Not Enough for AI Agents
- The PlainID Platform
- Secure Access Control in Power BI with PlainID
- BigID & Plainid Partner on Enterprise Data Protection
- PBAC and OWASP API Risks: Key Insights and Mitigation
- Consistent Data Access Control with PBAC
- PlainID Joins IDAC to Discuss Securing Agentic AI with Policy-Based Authorization
- Secured by Design: Building Trustworthy Agentic AI from the Ground Up
- Challenging the Status Quo: Why Agentic AI Demands a New Approach to Access Control
- What Is Open Banking Delegated Access?
- Data Compliance and MNPI: How to Protect Sensitive Information with PBAC
- Best Practices for Securing AI Systems with Authorization
- Best Practices for Securing AI Systems with Authorization
- OWASP Top 10 for LLM and GenAI Security with PBAC
- LLM & GenAI Security
- Why Policy-Based Access Control Matters for Identity Audits
- Why Authorization Standardization Matters to Security Leaders
- Central Policy Management of Access Controls Part 1
- What is Identity Security Posture Management?
- Modern Authorization for Cybersecurity & Data Compliance
- What Is Dynamic Authorization and Why It Matters
- The Evolution of Authorization Controls with PBAC
- Five Factors for Choosing a Modern Authorization Solution
- The Business Value of an Enterprise-Ready Authorization
- Identity-First Security in the Evolving Threat Landscape
Deepen Your Knowledge
Free weekly newsletter
Subscribe to the NHI & AI Identity Journal
The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week.
Bonus 33% off our NHI Course when you subscribe.