Semperis provides an identity security and cyber resilience platform focused on protecting critical enterprise identity infrastructure, including Active Directory, Entra ID and Okta. Its platform combines identity threat detection and response (ITDR), posture management, attack path discovery and identity disaster recovery to help organisations prevent, detect, respond to and recover from identity-based cyberattacks.
Key Capabilities:
- Identity Threat Detection & Response (ITDR): Monitor Active Directory and Entra ID for suspicious activity and malicious directory changes, and automatically roll back unauthorised changes.
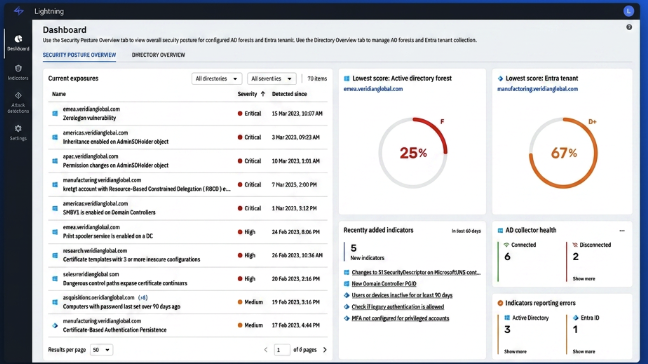
- Identity Security Posture Management: Assess identity infrastructure against continuously updated indicators to find misconfigurations, excessive privileges and exposures, and reduce the identity attack surface.
- Attack Path Discovery & Analysis: Identify and remediate attack paths leading to Tier 0 assets and highly privileged accounts.
- Non-Human Identity & AI Agent Security: Find and fix vulnerabilities in non-human and machine identities, control who or what can command AI agents, and detect and block misbehaving agents.
- Identity Disaster Recovery: Cyber-first recovery for Active Directory forests, plus backup and recovery for Entra ID and Okta tenants.
- Cyber Crisis Management: Coordinate incident response through an out-of-band crisis management platform designed to keep working when other systems are down.
- Identity Forensics & Incident Response: Expert services and forensics tools to investigate identity attacks and return identity systems to a trusted state.
Featured Content
Upcoming
Semperis Opens Call for Papers for HIP Conference Europe 2027 — Frankfurt, February 9
View event ↗ NewPrince of Persia: Threat Group Hiding in Plain Sight
Read article ↗ NewAD Group Risks: How Cryptographic Operators Dangers Escalate Quickly
Read article ↗ NewSemperis 2026 Ransomware Report Reveals Increases in AI-Driven Attacks and a Rise in Physical Threats Against Executives and Their Families
Read article ↗Further articles from Semperis
Showing 77 articles
- Change How You Protect Active Directory Service Accounts
- Reports
- What Should You Install on Your Domain Controllers?
- AD Group Risks: Hidden Powers of Account Operators
- Semperis Researcher Discovers Critical Active Directory Privilege Escalation Vulnerabilities
- Identity Crisis: Novel Vulnerabilities Leading to Kerberos Downgrade, DoS, and Full Domain Takeover
- How the Five Eyes AI Warning Changes Board Thinking About Cyber Recovery and Resilience
- Checklist: Prepare Your Identity Fabric for the Agentic Era
- AD Group Risks: Hidden Dangers in Backup Operators
- Midnight in the War Room: The CISOs’ Challenge Comes to the Screen
- The Minimum Viable Company Part 3: Enabling Visibility, Control, and Operational Resilience
- Practice Checkpoint 4: Verifying Tokens and Claims in 3 Entra ID Authentication Flows
- Practice Checkpoint 3: Registering an Agent—With and Without Agent ID
- The Agent Registry and How Agent Identities Operate in Entra ID
- Practice Checkpoint 2: Setting Agent Identity Permissions
- Agent Identities: Design Deep Dive
- Windows Privilege Abuse: How Attackers Escalate from Accounts with Dangerous Rights to Active Directory Compromise
- Practice Checkpoint 1: Building Agent ID with MS Graph
- Agent ID: Understanding Microsoft’s Agent Identity Platform
- The Taxonomy of Workload Identities in Entra ID: Service Principals, Enterprise Applications, and Other Forms of Organized Confusion
- Meet Entra ID Agent Identities (BTW: They’re Not People)
- Understanding and Preventing Entra ID Agent Identity Attacks: A Comprehensive Guide
- Bringing Identity Context Into the Microsoft Security Workflow: Semperis’ Integration with Sentinel and Copilot
- When the Lights Go Out: What the Foxconn Breach Tells Us About Identity-First Ransomware
- Semperis Appoints Jimmy McNary as Deputy Federal CTO to Drive Identity Security Strategy Across the Public Sector
- 11 Real-World Risks Hidden in Active Directory Migrations
- Hack The Box and Semperis Form Strategic Technology Alliance to Advance Enterprise Identity Resilience
- Zero Trust vs Breach Prevention: What’s Your Identity Security Objective?
- RC4 and AD Migration: Uncover the Break Scenarios Hiding in Your Source Domain
- New Semperis Study Reveals AI’s Effects on the Identity Attack Surface
- The State of Identity Security in the AI Era
- Semperis Names John Podboy Chief Information Security Officer
- Semperis’ Identity-Driven Security Platform Now Available Through Carahsoft’s SEWP V and ITES-SW2 Contracts
- Identity Resilience Checklist: 6 Ways to Think Beyond Backup
- What Good Looks Like: The Modern Model for Cyber Crisis Management
- The Minimum Viable Company Part 2: Cyber Resilience Lessons from Beyond the Breach
- Backups vs. Breaches: Entra ID Recovery Tools for Everyday Mistakes and Malicious Intrusions
- Purple Knight Now Delivers Comprehensive Identity Security Assessments for Microsoft GCC High Environments
- The Minimum Viable Company Part 1: Why True Cyber Resilience Starts with Identity
- The Missing Layer in Cyber Incident Response: Crisis Orchestration
- How to Audit Your Environment for RC4 Encryption
- Rethinking Cyber Crisis Management: Why Plans Fail — and What to Build Instead
- What You Need to Know: Windows Admin Center Remote Privilege Escalation (CVE-2026-26119)
- When Is WinRM Over HTTP Secure?
- What You’re Missing: Proper LAN Manager Authentication Levels
- Semperis Appoints Tom Linckens to its Strategic Advisory Board
- Hardening Entra ID Recovery and Identity Security Resilience
- Checklist: How to Assess Your Cloud Identity Environment for True Cyber Resilience
- LDAP, LDAPS, and Active Directory
- DORA Compliance and ITDR
- Understanding Identity Security Posture: See the Big Picture of Your Hybrid Environment
- How to Defend Against Password Guessing Attacks
- Introduction to Identity Forensics & Incident Response (IFIR)
- What is Identity Attack Surface Management?
- Unconstrained Delegation Explained
- Password Spraying Detection in Active Directory
- LDAP Injection Attack Defense: AD Security 101
- 25 Years of AD Breaches: Three Moves to Transform Incident Response
- SyncJacking: Hard Matching Vulnerability Enables Entra ID Account Takeover
- Ransomware Defense in 2026: What CISOs Need to Know
- Semperis and CGS CyberDefense Partner to Strengthen Enterprise Cyber Resilience
- NEW Semperis Study Reveals that the Majority of Ransomware Attacks Continue to Occur During Holidays and Weekends
- Unlocking Unmatched Identity Resilience: The Semperis-Cohesity Partnership
- Semperis and Forsyte I.T. Solutions Partner to Deliver Advanced Identity System Resilience for Education and Public Sector Agencies
- EntraGoat Scenario 1: Service Principal Ownership Abuse in Entra ID
- 5 Keys to Fault-Tolerant Active Directory Recovery
- Getting Started with EntraGoat: Breaking Entra ID the Smart Way
- What Is EntraGoat? A Deliberately Vulnerable Entra ID Simulation Environment
- How to Secure Service Accounts: Protecting Identity Security’s Achilles’ Heel
- Improve Hybrid AD Security with Automated Response and Streamlined Administration
- Semperis Research Uncovers Critical Flaw in Windows Server 2025 Exposing Managed Service Accounts to Golden dMSA Attack
- How to Block BadSuccessor: The Good, Bad, and Ugly of dMSA Migration
- 2025 Purple Knight Report Reveals Persistent Security Gaps in Hybrid Active Directory and Entra ID Environments
- Semperis and ADAPTIT Partner to Enhance Hybrid Identity Security for Leading Enterprises Across Greece
- Kerberoasting Explained
- Password Spraying Explained
- Golden Ticket Attack Explained
No articles match these filters.
Deepen Your Knowledge
Free weekly newsletter
Subscribe to the NHI & AI Identity Journal
The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week.
Bonus 33% off our NHI Course when you subscribe.