Secrets Security for Non-Human Identities
Truffle Security Co. helps organizations reduce the risk of secret sprawl. As the company behind TruffleHog, a leading open-source secrets scanning tool, Truffle Security Co. brings proven detection and verification to the challenge of securing non-human identities and their secrets. Through TruffleHog Enterprise, organizations see where secrets are exposed, understand the access they carry, and confirm when the risk has been eliminated.
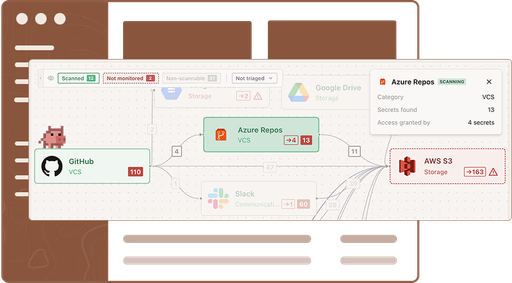
- Cross-stack secrets detection: Find exposed secrets across code and Git history, CI/CD, SaaS and collaboration tools, tickets and docs, cloud storage, and workstations.
- Liveness verification: Test findings against the provider to establish which secrets still authenticate as a working identity. Everything found stays visible; verification changes what raises an alert.
- Deduplication: Consolidate the same secret found in multiple locations into a single finding, since the identity behind it needs to be revoked once no matter how many copies exist.
- NHI discovery and access analysis: Map a verified secret to the non-human identity it authenticates, its permissions, and what it can likely reach, so teams prioritize by consequence rather than volume.
- Attribution: Trace a secret back to the person or team who can actually revoke the identity behind it, rather than whoever exposed it.
- Public exposure monitoring: Watch public sources outside the organization for live secrets that trace back to it, using the same detection and verification.
- Remediation: Route the request into their existing workflow with rotation guidance, then retest the secret, confirm it no longer authenticates, and record the outcome.
Featured Content
New
Revoking a Leaked Secret Doesnât Have to Be a Gamble
Read article ↗ NewIntroducing the Secrets Revocation Program: revoking 1.4 million live API keys
Read article ↗ NewThe Vault Governs the Secret. The Copies Still Work.
Read article ↗ NewTruffle Security Announces Collaboration with Google Cloud to Help Secure Exposed Secrets
Read article ↗Further articles from Truffle Security
Showing 54 articles
- Model Distillation: Why Attackers Want Your API Keys
- Focused S3 Scanning and OAuth2 Authentication in TruffleHog Enterprise October 2026 Release
- The Next Supply Chain Attack May Start With a Stolen Token
- AWS Key Quarantine is Not Revocation
- Leaked Credentials Let an AI Agent Into Two Companiesâ Systems
- One non-human identity, two states
- GitHub Repos Exposed 543,699 Credentials. Nobody Revoked Them.
- Why exposed credentials stay live for years
- AI Worms Are Coming Soon
- TruffleHog AWS Analyze press release â Truffle Security Co.
- Beyond Laptops: What secrets to expect on your endpoints
- 768 Leaked Corporate AWS Keys Held Full Admin Rights
- Introducing TruffleHog AWS Analyze: Know What a Leaked AWS Key Can Reach
- Admin on Apache Org Exposed for 2.5 Years in Deleted PyPI Package
- Guest Post: How I Scanned all of GitHubâs âOops Commitsâ for Leaked Secrets
- Google Fixes the Gemini API Key Privilege Escalation Issue
- Your PR scan is missing half the problem
- Scanning 1.2 Million DotNetFiddle Snippets for Secrets
- Scanning 7.6 Petabytes of AI Training Data for Secrets
- API Keys Leaking in PNG Metadata of AI Images
- CISA's Leaked Admin GitHub Token Remained Live 2 Days After Krebs Reported It Leaked
- Thousands of Live Secrets Found Across Four Cloud Development Environments
- Contributor Spotlight: Strengthening TruffleHog's SSRF Protections
- TruffleHog now detects JWTs with public-key signatures and verifies them for liveness
- The Rise of API Worms
- Scanning 5.6 million public GitLab repositories for secrets
- Scanning 2.6 million public Bitbucket Cloud repositories for secrets
- We've been doing NHI since 2016
- Contributor Spotlight: Adam Reiser of Cisco Talos
- TruffleHog in Your Logs?
- Detecting Exposed Secrets in Salesforce with TruffleHog
- Guest Post: GCP CloudQuarry: Searching for Secrets in Public GCP Images
- How to Scan Force Pushed Commits for Secrets
- Research finds 12,000 âLiveâ API Keys and Passwords in DeepSeek's Training Data
- Removing Jeff Bezos From My Bed
- Under the Hood: The Algorithmic Power Behind TruffleHogâs Secret Scanning
- Vigilante Justice on GitHub
- Mishandled OAuth Tokens Open Backdoors
- LLMs are Teaching Developers to Hardcode API Keys
- 7 Spooky Places Your Secrets Leak Online
- Secrets in Source Code Are Not A Code Security Problem
- Leaked Secrets in Public Jenkins Logs
- 11,000+ GitHub users' SSH keys are too weak
- Stop Recommending JWTs (with symmetric keys)
- Bug Bounty Hunting Leaked Credentials
- 74% of publicly leaked keys are never revoked
- Research Uncovers AWS Account Numbers Hidden in Access Keys
- Why did 1 GitHub Repo leak 5,000 Live GCP Keys?
- Think Twice Before Commenting: Thousands of GitHub Comments Leak Live API Keys
- How Secrets Leak out of Docker Images
- 4,500 of the Top 1 Million Websites Leaked Source Code, Secrets
- Do Pre-Commit Hooks Prevent Secrets Leakage?
- Deleting leaked API keys isnât a solution
- How Secrets Leak in CI/CD Pipelines
No articles match these filters.
Deepen Your Knowledge
Free weekly newsletter
Subscribe to the NHI & AI Identity Journal
The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week.
Bonus 33% off our NHI Course when you subscribe.